MAYAChain Halts After Six Bugs Are Chained in a Single Transaction — an Accounting Failure Where Only the Record of a Failed Transfer Survived
What happened
MAYAChain is a cross-chain liquidity network for swapping native assets across chains without a centralised exchange, built as a friendly fork of THORChain. CACAO is the common asset connecting its liquidity pools.
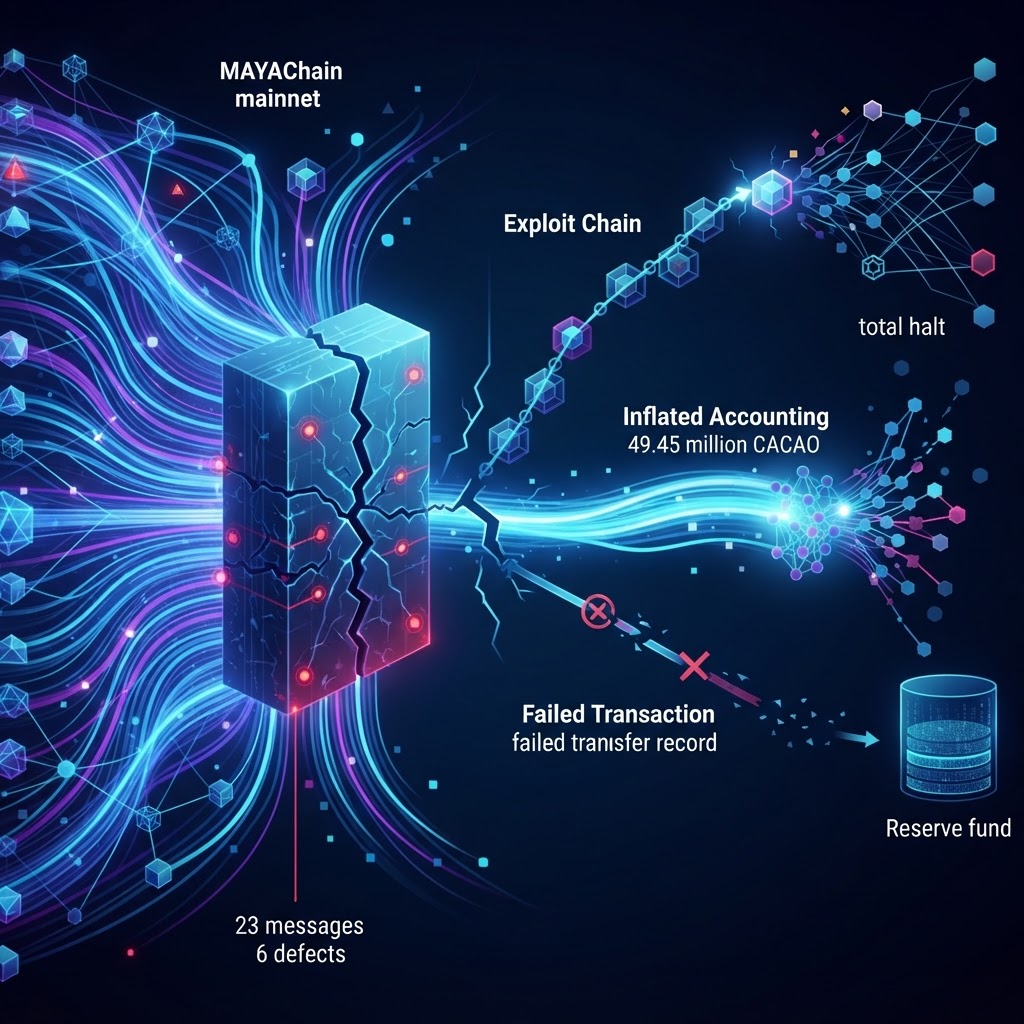
Per the team's preliminary post-mortem, the attack began at approximately 17:30 UTC on 2026-08-18 with a single MsgDeposit transaction containing 23 messages. The team describes it as a chain of six defects running through the protocol's trade account and outbound transaction handling logic.
The sequence runs as follows. MAYAChain failed to correctly recognise that certain withdrawals had already been executed. That failure incorrectly triggered the theft-detection mechanism, which is paired with a slash subsidy intended to compensate a pool for the loss — and the subsidy was uncapped. As a result, roughly 49.45 million CACAO was credited to a low-liquidity pool even though the reserve held only about 168,000 CACAO. The transfer itself failed, but the inflated balance had already been saved, so the network kept treating the pool as holding the extra tokens.
The attacker then deposited a small amount into the distorted pool, ended up owning 99.93% of it, and withdrew 48.87 million CACAO from Maya's Asgard module — then swapped it for BTC, ETH and other assets sitting in MAYAChain's pools.
Two different amounts are in circulation. The attacker's direct proceeds were about $1.65 million: roughly $1.36 million (about ¥220 million) moved to external chains and about $291,000 (about ¥46 million) left on-chain. Founder AaluxxMyth described it as 20 BTC (about $1.4 million) plus roughly $300,000 in other assets. Separately, total pool losses once the CACAO sell-off and arbitrage are included are estimated at roughly $10.9 million (about ¥1.73 billion). These are different quantities and must not be added together. CACAO traded around $0.115 before the attack and fell roughly 88–89% afterwards.
The team halted the chain globally within hours of detection, pausing BTC swaps and other cross-chain operations. As of 21 August the network remained halted or in maintenance while fixes for all six defects were worked through. A white-hat bounty has been offered to the attacker.
Comparison and the general lesson
The same month, the bridge connecting tx (formerly Coreum) and the XRP Ledger lost roughly 199,900 XRP to a deposit-verification flaw. The structure overlaps with Maya's: an off-chain relayer or accounting layer accepted as proof of a legitimate deposit something it should not have.
What both share is that the place assets are held and the ledger recording how much is held are different objects. Maya's Asgard is the side that actually custodies native assets from other chains; a pool balance is the ledger that references it. In THORChain-family designs, safety rests on those two layers agreeing. Rewrite the ledger alone and you can carry off real assets from the custody side as a legitimate withdrawal. The attacker ended up with BTC and ETH precisely because a CACAO balance on the ledger functions as a claim on Asgard's real holdings. In this class of design, the quantity to monitor is therefore not the ledger's internal consistency but the gap between ledger and custody.
Generalised, the same error appears at three layers.
First, logic that issues value under exceptional conditions — compensation, slashing subsidies, rebates — did not reference the issuer's actual balance. Maya's subsidy credited 49.45 million CACAO while the reserve held 168,000. An uncapped compensation path delegates the protocol's solvency to the accuracy of whatever detection heuristic triggers it. Detection will be wrong sooner or later; the correct design pins the issuance ceiling to the issuing account's real balance, outside the detection logic.
Second, a failed operation left state changes behind. The transfer failed, yet the inflated balance persisted. This is the same shape as the cosmos/evm incident disclosed the same week, where the root was likewise that one value was written through several paths and only one side got updated. Rollback on failure paths is not exercised by success-path tests. As long as test coverage is skewed toward the happy path, this class of defect survives.
Third, allowing multiple messages in a single transaction gives an attacker freedom to chain state transitions inside one atomicity boundary. Individually, none of the messages need violate an invariant; the combination of 23 does. Any implementation that checks invariants per message but commits per transaction has this gap structurally.
Pitfalls to watch
First, this looks like value created from nothing, but total supply never increased. What increased was one pool's recorded balance; what was actually removed were assets genuinely held in the Asgard module. Supply monitoring will not detect it. The quantity to monitor is the gap between a pool's recorded balance and the reserve or module balance backing it.
Second, reported losses range from $1.65 million to $10.9 million because the aggregates differ. Attacker proceeds, pool economic loss and CACAO-denominated nominal value are three different quantities — and because CACAO collapsed during the attack, the figure moves depending on which price timestamp is used. Quoting a single number internally guarantees an inconsistency when someone meets a different one.
Third, the attacker's own selling crushed the CACAO price, which limited what could ultimately be extracted. That is a side effect of thin liquidity, not a defence working. "Losses were small, so the design held up" does not follow.
Fourth, the global halt stopped further damage, but during a halt user funds cannot move either. Stopping cross-chain processing also means operations in flight on other chains may complete on one side only. Integrators connected to Maya need to check for swaps that settled on one side during the halt.
Fifth, white-hat return negotiations have both succeeded (Euler Finance in 2023, roughly $197 million) and failed. Building a recovery plan that assumes return means rebuilding the whole plan if negotiations stall.
[Technical Insights & Actions]
- Logic that issues value under exceptional conditions — compensation, slash subsidies, rebates, insurance-style top-ups — turns any error in its triggering heuristic into unbounded issuance unless the ceiling is pinned to the issuer's actual balance. Detection will be wrong, so the ceiling has to live outside the detection path. This applies to every protocol implementing slashing or compensation, not just Maya. [Protocol developers] By the next release, enumerate every path in your protocol that conditionally issues or moves value, verify that each one's ceiling is bound to the issuing account's real balance rather than to a detection result, and file the unbound paths as defects.
- Designs where a failed operation leaves part of its state change behind are not caught by success-path-weighted testing. Here, the transfer failed and only the inflated balance persisted. The same structure appeared in the cosmos/evm incident, which makes it reasonable to treat this as a cross-industry defect class. [Contract and chain developers] During September, enumerate the points where an external call or transfer can fail and add test cases verifying that no accounting side effect survives a failure. Measure failure-path coverage, not overall coverage.
- Where multiple messages are allowed in one transaction, invariants can break through combinations of individually legitimate operations unless the invariant check boundary matches the commit boundary. [Protocol teams / auditors] Place invariant checks at the transaction boundary (immediately before commit) as well, and add fuzzing over multi-message transactions to the pre-restart test plan.
[Sources]
- Maya Protocol, preliminary post-mortem and founder AaluxxMyth's posts (2026-08-18 to 08-19), as reported by Decrypt: https://decrypt.co/375976/maya-protocol-halts-network-bitcoin-exploit
- PrimeXBT, "Maya Protocol Halts Network After Six-Bug Exploit" (the 168,000 CACAO reserve and the 49.45 million CACAO credit) (August 2026): https://primexbt.com/news/maya-protocol-halts-network-after-six-bug-exploit-drains-1-7-million-cacao-plung/
- crypto.news, "Maya Protocol suffers $1.7 million exploit, halts network" (the 23-message transaction) (2026-08-18): https://crypto.news/maya-protocol-suffers-1-7-million-exploit-halts-network/
- Cryptopolitan, "Maya Protocol loses $1.7M in sophisticated six-bug exploit" (timeline and figures): https://www.cryptopolitan.com/maya-protocol-loses-1-7m-bug-exploit/
- Shattered, "Maya Protocol Hack Drains $1.7M, CACAO Crashes 88%" (attack timestamp, white-hat bounty, comparison with the tx / XRP Ledger bridge incident) (2026-08-21): https://shattered.io/maya-protocol-hack-cacao-crash-2026/
This article is a technical commentary based on publicly available information and is not investment advice.