A Range-Proof Verification Cache Bug Let Liquid Network Mint Roughly 4,000 BTC of Unbacked L-BTC
What happened
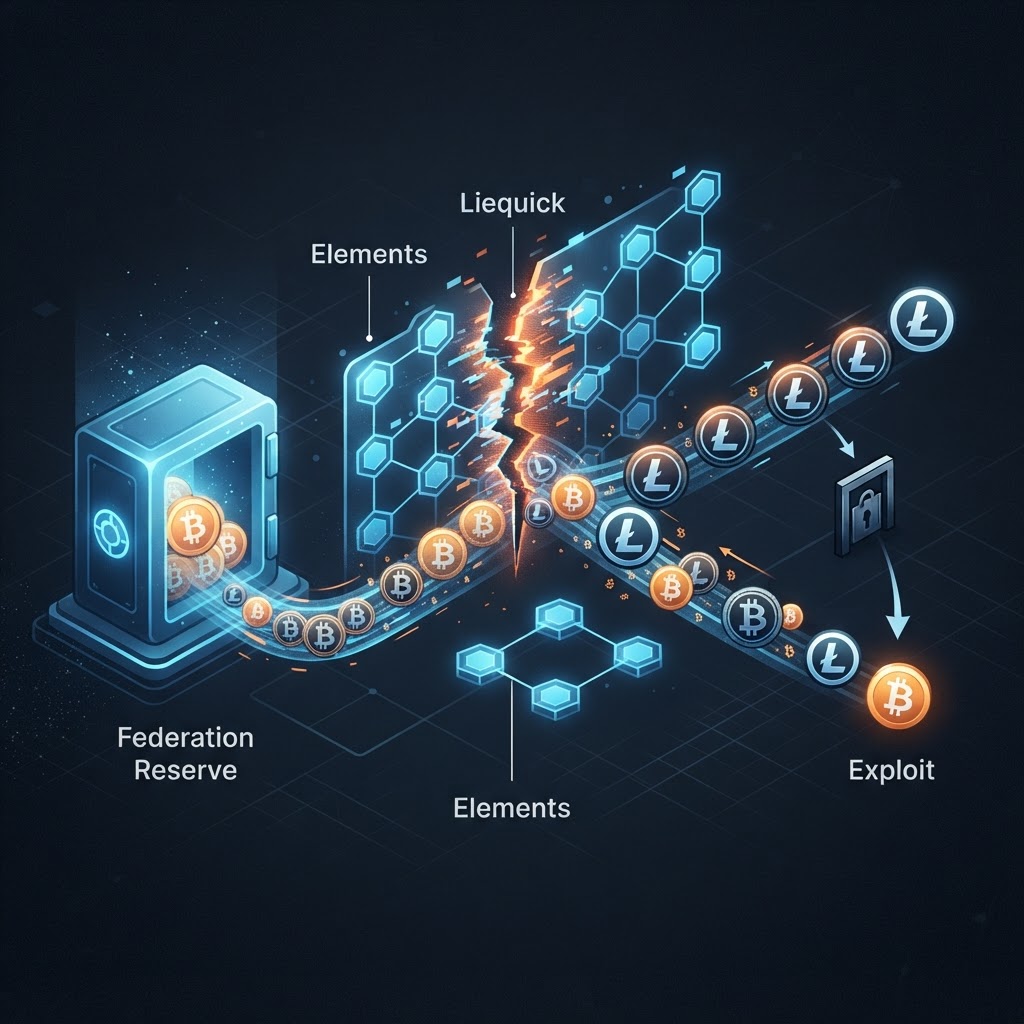
Liquid is a federated Bitcoin sidechain built and operated by Blockstream, in which L-BTC is meant to be backed one-for-one by BTC held by the Federation. According to the official incident report (status as of 2026-09-08 19:10 UTC), a vulnerability related to how Liquid nodes cache range-proof verification was exploited at Liquid block 4,050,336 on 2026-09-06 at 15:53:10 UTC. Blockstream has characterised the root cause as a cache-key collision in confidential transaction verification logic.
Liquid uses confidential transactions, which hide amounts. The guarantee that an output amount is non-negative rests on a range proof. Verifying those proofs is expensive, so results are cached — and if the cache key does not uniquely identify what was verified, a previous successful verification can be reused for something that was never actually checked. The result here was the creation of roughly 4,000 BTC worth of L-BTC with nothing behind it.
The forged L-BTC was then converted to real BTC through SideSwap's standard peg-out path. SlowMist records the loss at about 4,000 BTC, roughly USD 320 million at the time (about JPY 48.7 billion at 152.27 JPY/USD, Google Finance, 2026-09-13), which implies a BTC price near USD 80,000. Third-party reporting puts the reserve at roughly 4,200 BTC before the incident; if accurate, about 95% of the reserve left in a single event. Blockstream states that the Federation's signing keys were never compromised.
How the attack came together
Three things had to line up: a cache introduced to cut verification cost, a key that failed to establish identity of the verified object, and a direct path from that failure to the heaviest invariant in the system — the supply cap on issued L-BTC. Crucially, the peg-out path itself worked exactly as designed. Nothing looked anomalous at the point of withdrawal; to the Federation it was a valid redemption of valid L-BTC.
The response was fast. The patch to the bridge nodes was completed at 01:09 UTC on 2026-09-07, about 9 hours and 16 minutes after the exploit. The actor left a message on the Bitcoin mainchain identifying themselves as a white-hat researcher and returned 3,400 BTC to the Federation peg wallet at 16:09:25 UTC on 2026-09-07. Roughly 598.5 BTC — about 15% of the total, near USD 47 million (about JPY 7.16 billion at the same rate) — remains outstanding. On 2026-09-09 the actor demanded on-chain that Blockstream pay a 10% bounty out of its own funds or holders would take a 15% loss. Blockstream refused, calling the conduct theft rather than responsible disclosure, and said it would work with law enforcement, exchanges and forensic firms.
The network stopped. Third-party observers recorded the chain tip frozen at block 4,051,232 — 896 blocks past the exploit block, roughly 15 hours at the nominal 60-second interval — with no blocks produced for more than a day. The emergency Elements v23.3.4 release was published at 13:30 UTC on 2026-09-09 and block production resumed, while peg-in and peg-out remained suspended. CEO Adam Back has stated publicly that the 1:1 L-BTC peg will be covered.
Verification caches are a recurring weak point
The generalisable lesson is that caching quietly substitutes a weaker premise for a stronger one. When you cache a cryptographic verification, you are asserting that the cache key fully captures the conditions under which the result holds. If a proof format is extended, or only part of a commitment makes it into the key, you get a state in which verification appears to have passed but nothing was verified. The same class of bug has appeared in bridge signature caches and precompile result caches; this is not specific to Liquid.
The second generalisation is that in federated or multisig bridges, "the keys are safe" does not mean "the assets are safe." The keys here were never touched. What was compromised was the upstream logic that decides what the keys are allowed to sign for. Any team that scores bridge safety purely by the diversity of the signer set is missing an axis.
Having the option to stop
What stands out in the response is how quickly halting block production became available as a choice. On a federated sidechain the block signers are a known set, so agreement to stop can be reached fast. Public proof-of-stake and proof-of-work chains have no equivalent; there is essentially no way to pause while an incident is in progress. That the loss stopped near 4,000 BTC, and that a negotiation returning over 80% of it became possible, rests in part on that capability.
But the same capability is a trust assumption. From a user's point of view, the operator can render their assets immovable — which in ordinary times is simply centralisation. This incident is a concrete case of that authority limiting damage; what guarantees it will not be used for some other purpose on some other day lives in governance, not in the protocol. When evaluating a bridge or sidechain, "it can be stopped" belongs in both the strengths and the weaknesses column, and an assessment that records only one of them is incomplete.
The handling of the return negotiation is worth recording as well. The actor approached on-chain calling themselves a white hat and demanded a bounty; Blockstream classified this as theft and refused. That judgement bears on an industry-wide line: whether holding assets conditionally counts as responsible disclosure. Accept it and you effectively publish a price list for the same behaviour. Refuse it and the incentive to return funds rests on law enforcement and tracing risk. Both have side effects, and this outcome will be cited in the next case of its kind.
Pitfalls to watch
First, monitoring L-BTC backing by watching the BTC balance in the Federation wallet would not have caught this. The balance only fell after the peg-out executed; the anomaly existed earlier, on the issuance side. What matters is the delta between issuance and backing — and on a confidential chain, the issuance side cannot simply be summed.
Second, resumed block production is not resumed service. While peg-in and peg-out stay suspended, L-BTC can move within the chain but cannot enter or leave as BTC. Exchanges and wallets whose health check is "is the chain producing blocks" will show users an availability that does not exist.
Third, the treatment of the roughly 15% that was not returned is unresolved. Blockstream has said the peg will be covered, but as of this writing the source of funds and the mechanics have not been published. Protocols accepting L-BTC as collateral should assume valuation uncertainty until backing is publicly restored.
[Technical Insights & Actions]
- A verification cache whose key does not uniquely identify the verified object mass-produces the lie "already verified," at speed. Anywhere your own code memoises signature checks, proof checks or access-control decisions, the question is whether you can demonstrate that inputs excluded from the key cannot change the result. [Node operators / protocol engineers] This week, inventory every cache key in your verification paths and pin down with tests that inputs outside the key cannot alter the verification outcome.
- Key safety does not imply asset safety. A bridge threat model written only around signer-set decentralisation omits the path taken here: a defect in the upstream logic that determines what gets signed. Legitimate keys signed an illegitimate request that looked legitimate. [Integrators] Within the month, add non-key failure paths — issuance logic, verification caches, forwarding logic — to the threat model for each bridge you depend on, and record who holds the pause authority and under what conditions it fires.
- The health of a wrapped asset is measured by the gap between issuance and backing, not by custodial balance. Balance monitoring is inherently after the fact and blind to issuance-side anomalies. On confidentiality-preserving chains, external verification of issuance is hard — and that difficulty is itself a risk factor. [Product and risk management] Within two weeks, determine for each wrapped asset you handle whether issuance can be reconciled against backing from outside; where it cannot, revisit credit limits and collateral haircuts.
[Sources]
- Liquid Network (@Liquid_BTC, incident report) (2026-09-08): https://x.com/Liquid_BTC/status/2097404704028545175
- SlowMist Hacked (incident database, 2026-09-06 entry): https://hacked.slowmist.io/
- Blockonomi, "Liquid Network Exploit: Blockstream Recovers 3,400 BTC" (2026-09-09): https://blockonomi.com/liquid-network-exploit-blockstream-recovers-3400-btc-after-400m-bug
- Blockonomi, "Blockstream Takes Hard Stance Against Liquid Network Hackers" (2026-09-11): https://blockonomi.com/blockstream-takes-hard-stance-against-liquid-network-hackers-demanding-ransom-for-598-btc
- The Cryptotimes, "Liquid Network Restarts After $320M Exploit" (2026-09-10): https://www.cryptotimes.io/2026/09/10/liquid-network-restarts-after-320m-exploit-adam-back-says-lbtc-peg-will-be-covered/
- The Industry Spread, "Liquid sidechain stays frozen after 3,400 of 4,000 BTC returns" (2026-09-08): https://theindustryspread.com/liquid-sidechain-frozen-3400-btc-returned-blockstream-sideswap-pak/
This article is a technical commentary based on publicly available information and is not investment advice.